Exploring Risk Assessments:
A CFO’s Reference Guide
Introduction
Whether you know it or not, you open yourself up to risks every single day—even through seemingly mundane activities.
Picture this: you’re in New York City waiting to cross a busy, one-way intersection at Times Square.
At this intersection, there are various lanes for cars, bikes, and buses, along with a traffic light and crosswalk. The crosswalk is approximately 91 feet long.
Taking the threats of each of those conditions into consideration, here’s what could happen:
- Potential to be hit by a car or motorcycle
- Potential to be hit by a bike
- Potential to be hit by a bus
- Potential to come into contact with another pedestrian
- Potential to fall into an open manhole or have an issue with a sewer or a subway grate
Based on these threats, what decision-making process would you follow to reach your destination?
This thought process is the first step in performing a risk assessment: evaluating the conditions and threats associated with a specific scenario.
In your role as a fractional CFO, it’s essential to encourage clients to identify risks, understand threats, and take steps to mitigate them. After all, proper risk management is a key aspect of any CFO’s role.
To help you navigate these conversations and responsibilities, we’re sharing key concepts regarding risk and risk assessment frameworks.
We’ll also explore the main types of risks and the importance of championing proper risk management for your clients.
What are Risks and Risk Assessments?
Knowing the basics of risk and risk assessments is essential for building a solid foundation of mutual understanding between you and your clients.
Whether your clients work with an external provider to complete the assessment or have an internal team, it’s important to know exactly what contributes to risk and what a risk assessment includes.
What is Risk?
A risk is the possibility of loss, specifically something of value, as a consequence of an action or situation.
Any risk requires several conditions:
- Something of value
- A specific action or situation
- A degree of uncertainty
Humans assess risk all day long, as seen in the New York City crosswalk example.
Laying out the most reasonable possibilities and analyzing each of them is the first step in any risk assessment.
Every one of these threats can be examined in greater detail. For instance, you would likely have a lower probability of being hit by a bike, as it’s much easier to avoid that than to avoid being hit by a car in an intersection with three lanes of traffic.
However, if you were taking a walk on a cycling trail, the risk of being hit by a bike would increase immensely because of the altered conditions.
When an organization begins quantifying, analyzing, and ranking potential threats, the analysis turns into a risk assessment.
What is a Risk Assessment?
A risk assessment is an evaluation of all reasonable threats to an organization. This process includes identifying potential threats, ranking them in terms of likelihood, severity, and criticality, then engaging in risk mitigation planning.
Ultimately, this process will drive a decision in a particular scenario, whether that’s instituting additional controls, doing nothing, or removing the risk entirely.
Done correctly, a risk assessment will provide objective numbers for the likelihood and impact of specific scenarios. It will also provide justification for any reasoning with current controls.
These risks can range from cyber threats to natural disasters to instances of human error.
Working with a trusted provider can be a smart choice for your clients, as these experts have completed these steps before for other businesses.
When beginning any risk assessment, you’ll want to ensure the provider objectifies what each number means and stays consistent throughout the assessment. That way, you can gain meaningful results that clearly share residual risks and their corresponding threat level.
Risk assessments should also be practical and tied to the organization’s specific context.
For example, measuring the risk of “facility interruption” for a fully remote, cloud-native organization with no servers may not be as beneficial as measuring the risk of an issue or interruption to a user’s laptop in that case.
Your clients’ assessment should focus on risks that actually apply to their organization as opposed to applying generic risks that may not be contextually relevant.
Understanding Inherent vs. Residual Risk
The goal of any risk assessment is to influence residual risk—exploring Inherent Risk and Residual Risk can help you understand the purpose of a risk assessment and associated controls.
Inherent Risk refers to the risk present without any security controls in place. Any controls applied can reduce it to Residual Risk.
Inherent risk relates to residual risk like this:
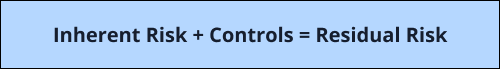
Ideally, this would involve taking a situation that, without the right controls, could be considered risky. Left unchanged, these risks could lead to downtime, financial costs, and reputational damage.
Your clients would apply controls to that situation in an effort to reduce the residual risk to a point that they could accept it and any associated consequences. You can help them determine the financial impact they could withstand.
Controls can change a variety of risk factors. They can affect the likelihood of the threat occurring, the impact if it does occur, and the criticality of that threat—specifically, how the organization copes with the event.
By helping your clients understand the outcome of a risk assessment, you can ensure that they frame the process appropriately from the beginning.
What is the Risk Assessment Methodology?
The risk assessment methodology involves sensitive information flow mapping and an assessment based on the NIST 800-30 framework.
Combining the information map with the risk assessment framework will give your clients a clear view of their organization’s current state and levels of risk.
Sensitive Information Flow Mapping
Sensitive information flow mapping identifies exactly what data moves where and with whom. It functions as one element of a risk assessment, seeking to understand what business units intersect and the types of sensitive information they share.
Done correctly, a sensitive information map details how internal reporting and third parties are involved in data sharing and where the information comes from.
Often, seeing this map visually makes it clear that there are more systems or more controls in place than a business might have originally thought.
A complete map also makes it easier to objectively view the current control environment’s controls without overrelying on open-ended questions.
Once sensitive information flow mapping is complete, you can begin evaluating threats using the NIST 800-30 Framework.
NIST 800-30 Framework
The NIST 800-30 framework is a methodology often used for structuring risk assessments. It was created by the National Institute of Standards and Technology, which also publishes the NIST Cybersecurity Framework.
NIST 800-30 functions as an objective way to understand risks and evaluate a specific organization’s environment.
Specifically, it helps businesses clearly understand the likelihood, severity, and criticality of a specific threat occurring based on the existing controls:
- Likelihood: How probable is it that this specific threat will occur?
- Severity: If the threat occurred, how severe would the impacts be on the organization?
- Criticality: Would the organization still be able to run and function properly in the event of this threat taking place?
From there, the overall risk score for that threat can be determined.
At the end of the assessment, threats can be clearly ranked and prioritized based on their overall risk scores. This ranking provides a clear path to mitigation steps, allowing organizations to prioritize remediation efforts accordingly.
By quantifying these threats, your clients will understand the best ways to reduce residual risk and protect their businesses.
Types of Risks: Operational Risk vs. Strategic Risk
When evaluating risks, it’s important for your clients to understand the types that they face and how they can potentially impact each other.
Operational risks represent acute, day-to-day actions and decisions. You make decisions involving operational risk every day, like deciding whether it’s safe to cross the street.
For a business, an operational risk might be associated with handling an unusual email request to direct funds to a different account.
Strategic risks are broader in scale and bigger picture, helping to drive whether a specific action should be taken at all.
In everyday life, strategic risk would factor in a variety of parameters.
Let’s change the earlier scenario of crossing the street and say that instead of a busy NYC street intersection, you’re approaching a controlled highway intersection on a bike.
Some of the parameters from earlier would go away; you’d no longer need to worry about lots of pedestrians being around or many city buses moving down the street. However, some of the elements would be the same as the NYC example, like your visibility to drivers.
Let’s consider some of the components in this scenario:
- The amount of traffic on the road
- How visible you would be to drivers
- The condition of the bike
- Weather and road conditions
In addition, although you’re still crossing the street, this example shows how altering the situation (e.g. location, transportation type) changes the elements and their associated risk.
These items would dictate whether or not you would even be in the operational risk situation in the first place. In this case, these elements might dictate that the day is not suitable for a bike ride.
For a business, an example of a strategic risk might be deciding whether to hire a third-party accounting firm. That would reshape the way your finances are run, how funds are directed to accounts, and who manages accounting activities.
This decision would impact whether or not you would face the operational risk of a fraudulent wire transfer.
Choosing to handle finances differently might remove that possibility from occurring entirely.
A risk assessment evaluates both operational and strategic risks and helps your clients understand how they relate to each other.
In summary:
- Operational risks represent day-to-day actions that a business faces every day
- Strategic risks represent broader, large-scale actions that can directly impact operational risks
Threat Categorization
Every organization faces an infinite number of threats to any organization and a limitless scope of impacts. The same threat can actually impact a business in any number of different ways.
This is where threat categorization comes into play, as it can help your clients understand where to focus their attention and controls.
As a fractional CFO, it’s important to understand that each threat could lead to financial loss; even accidental actions can cause breaches, downtime, and financial penalties.
Generally, threats fall into three categories:
Purposeful
Purposeful threats come from a place of intention; they do not happen accidentally.
They can include:
- Unauthorized access by an outside or inside party with malicious intent
- Lawsuit against a party, like employee to employer or customer to vendor
- Unauthorized exfiltration of data or funds
- Actions taken by a disgruntled employee
- Vandalism, break-in, theft
- Any misuse of permissions or rights within a system or over data
To combat these threats, organizations typically use human-centric controls. These are applied on the user level to reduce the likelihood of a threat occurring.
Unintentional
Unintentional threats occur purely by mistake. They may be accidental or the result of a lack of formal instruction or direction.
Examples of unintentional threats include:
- Accidental electronic disclosure of sensitive data
- Requests for system access not commensurate with job position or business necessity
- Abrupt/unplanned loss of a key stakeholder
- Risk of breach due to an uncontrolled work environment
Controls for unintentional threats typically don’t account for reducing the likelihood of the threat occurring. Instead, they address the impact if the threat comes to fruition.
Environmental
Environmental threats are based on the surrounding circumstances or context for a particular organization. They occur because of where an organization is.
They can include:
- Natural disaster
- Short/long-term facility access interruption
- Short/long-term power outage
- Network equipment or server equipment hardware failure
In these cases, avoiding the risks entirely is not always possible.
Taking steps to avoid risk entirely could actually change the impact of other threats that were not previously an issue.
Consider this example. Say a business moved their company office from Florida to Kansas to reduce the risk of hurricanes. While they would lower the threat of being impacted by a hurricane, their susceptibility to a tornado disaster would increase significantly.
Threat categorization is valuable to help your clients understand the nature of the risks they face and whether they can be avoided.
We’ll now explore risk acceptance and risk avoidance in more detail and how that relates to your clients.
Post-Risk Assessment: Risk Acceptance vs. Risk Avoidance
As your client wraps up their risk assessment and makes decisions about the right next steps, there are three main paths they can take: risk acceptance, risk acceptance with compensating controls, and risk avoidance.
Risk acceptance means that a business takes comfort in its current set of controls and their ability to thwart a reasonable attack and defend the system in place.
It acknowledges that although certain threats still remain, avoiding them entirely would be incredibly inconvenient or not make sense for the organization.
Risk acceptance with compensating controls means that a business is implementing relevant controls to reduce the likelihood or impact of the threat.
Risk avoidance refers to removing the target or stopping an activity entirely to avoid some type of risk entirely.
Consider this example to see how risk acceptance and risk avoidance connect to each other:
Say your client’s business had an office location in Midtown Manhattan. That location opens your client up to a variety of risks associated with the high population, geographic area, and infrastructure setup.
Yet, the office is near five of the business’s top clients, which proves valuable for maintaining relationships and visibility.
In this scenario, risk acceptance would mean acknowledging that threats would not change at the Manhattan location and implementing additional controls to defend against them.
These controls could be offering a work-from-home program, setting up a non-local infrastructure, and removing dependencies on the office location for most activities.
Risk avoidance would mean moving the office location entirely away to a more remote location.
Although your client would minimize the risks associated with the NYC location, it might open up additional risks in that new location.
It would also move employees further away from major clients, which could potentially negatively impact the business.
Working with a trusted expert can help your clients understand where risk acceptance, with the appropriate controls, makes sense.
Risk Assessments + Vulnerability Assessments
Augmenting risk assessments with vulnerability assessments is an important step to ensure the practicality of accepted or avoided risks.
A vulnerability assessment provides data on an organization’s actual “attack surface” through internal and external scanning.
On the other hand, a risk assessment evaluates threats from a conceptual standpoint.
Vulnerability assessments allow an organization to quantify where the real attack surface may lie, driving informed decision making. Specifically, it delineates how adding controls or shifting current controls will impact the organization.
The Financial Significance of Risk Assessments
Risk assessments are an important way for any organization to gain a deeper understanding of its vulnerabilities and the appropriate controls.
However, these evaluations take on an added layer of significance in your role as a fractional CFO.
Proper risk management is critical to your role—if your clients don’t take the right precautions, they could be impacted by events like cyberattacks and natural disasters. Left unprepared, they could face major financial fallout.
Just one minute of business downtime can cost small businesses $427. Multiply that over a few hours of downtime, and your clients could be facing a massive financial loss.
If your clients are in regulated industries, they may incur costly regulatory penalties if they’re found to violate standards like HIPAA or PCI. These fines are only increasing, with IBM noting their rise in 2025.
Reputational damage is more difficult to quantify, but can have a major impact. Customers can lose trust in businesses that experience a cyberattack, leading to loss of business and an associated decrease in revenue.
For instance, one company experienced a 31% decrease in stock price within a week of a public breach.
In addition, a 2024 UK survey found that almost half of businesses found it harder to bring in new customers after a cyber incident.
Make sure your clients understand how unaddressed risks open their businesses up to security vulnerabilities and major financial costs.
As a trusted advisor to your clients, you have the level of authority to ensure they take a proactive, forward-thinking approach to cyber risk management.
Ensuring Better Prioritization & Risk Communication
In your role, you occupy a unique niche for your clients; Oracle refers to the CFO as an “organization’s risk management steward.”
Though you’re not strictly in the cybersecurity domain, you need to have a strong understanding of best practices in order to mitigate risk effectively.
Working in tandem with IT leaders and third-party experts, you can help your clients better understand risk levels and accurately prioritize investments as a result.
The following items are additional ways you can help your clients adequately defend against threats.
Allocate Budget for Security Improvements
In your role, you’ll be able to help build a budget for security controls that aligns with current risks and organizational goals.
Using the risk assessment and other projections at your disposal, you can help make the right budgeting choices.
Where should the organization place the most focus, based on their risk assessment results? Are these improvements adequately contributing to risk reduction goals?
Your clients should partner with trusted experts to rank focus areas and implement the most important measures first with the help of a prioritized list or framework.
Communicate Risk in High-Level Terms
As you interact with C-suite members of your clients’ organizations, you should be able to clearly communicate risk and impact in terms that they’ll understand.
In other words, you need to translate technicalities into clear financial outcomes.
Directly connecting risks to financial consequences can help make the case for stronger protection and greater investment in cybersecurity.
Final Thought
Risk shouldn’t be viewed as a separate IT problem for your clients; it represents a major financial cost to their organizations, affecting business operations and longevity.
As a proponent of strong risk management, your role as a fractional CFO includes building risk-informed budgets and strong governance strategies.
By completing a risk assessment, your clients can bridge gaps and understand & prioritize areas of improvement.
When you continue to track these metrics over time, you can ensure your clients are well positioned to handle the most relevant threats.
Looking for guidance with assessing risk at your clients’ organizations? Contact our team today to connect with a risk expert.
Frequently Asked Questions
Why should a fractional CFO be involved in risk assessments?
A CFO or fractional CFO should be involved in risk assessments because their role involves risk mitigation planning, boosting operational efficiency, and controlling costs. This role enables them to build a proper budget for security controls and demonstrate the ROI of security improvements. They can also demonstrate the value of cybersecurity investments by translating technical information into clear financial outcomes that are easily understandable by other decision makers.
How does sensitive information flow mapping improve a risk assessment?
Sensitive information flow mapping is an important first step in any risk assessment. It is the process of identifying exactly what data moves where and with whom.
An organization cannot accurately assess risks if it is unclear where the data lives, how it is shared, or who interacts with it. This mapping ensures the assessment is based on the actual flow of information rather than an assumption.
How do operational and strategic risks impact daily business decisions?
Remember that operational risk focuses on acute, day-to-day actions and decisions. This impacts daily activities, like deciding how to handle an unusual email request to redirect funds to a new account.
Strategic risk focuses on broader, big-picture conditions to determine if an activity should be undertaken at all. This could include deciding whether to host servers on-premises or in the cloud, or whether to hire a third-party accounting firm.
These strategic decisions dictate the types of operational risks a business will face.
What are the three post-assessment options for handling risk?
The three post-assessment options are acceptance, acceptance with compensating controls, and avoidance.
- Accept the Risk: Acknowledging that a risk exists and deciding to tolerate it without further action
- Accept the Risk with Compensating Controls: Implementing relevant controls to reduce the likelihood or impact of the threat.
- Avoid the Risk: Removing the target or stopping the activity entirely to eliminate the specific threat.
When is risk avoidance a better strategy than applying controls?
When the controls cannot actually change the residual risk due to the fact that some conditions cannot be changed, risk avoidance might be the better strategy.