A CFO’s Guide:
The Balance of Security Posture
Introduction
As a fractional CFO, you may feel you’re walking on a high wire much of the time—and it’s not just from managing multiple clients.
Perhaps one of the largest balancing acts is effectively managing risk and maintaining a reasonable security posture.
It’s no secret that today’s companies face pressure from many different areas, from rising cyber risks to increasing regulatory requirements. Budget constraints and evolving cyber insurance markets add even more layers to this challenge.
This makes your role as a trusted advisor crucial: you need to help your clients adequately balance proactive and reactive cybersecurity controls, all while building a strong cyber resilience strategy.
To help you easily navigate these conversations, we created a guide explaining the value of proactive and reactive controls and how they work together to produce the most consistent security posture.
Our goal is to provide a clear approach so you can empower your clients to make the best cyber risk management decisions.
Proactive and Reactive Security Controls: Understanding The Continuum
As you work with clients to understand the state of their current security posture, it’s important to examine the different categories of security controls.
Though proactive and reactive security controls for an organization are equally important, they may not actually bear equal weight.
For clarity, consider the potential costs and effectiveness of proactive controls such as the implementation of MFA, deployment of an Endpoint Detection and Response (EDR) platform, or the use of Conditional Access policies to further enforce company device controls.
While examining these, we should not lose focus on the reactive elements, including cybersecurity insurance, Managed Security Services Provider (MSSP) alignment, or an Incident Response (IR) firm retainer as well.
The reality: each of these elements has a specific place along the continuum—no single one is the most important.
The combination of these controls working in concert with one another produces the most consistent security posture.
The Pitfalls of “Reactive Only” Controls
“An ounce of prevention is worth a pound of cure,” but what if you don’t invest in that ounce?
Organizations may lean heavily on reactive controls (cyber insurance, IR Firm, MSSP) for a variety of reasons, but cost and convenience tend to lead that pack.
Consider what happens when an organization focuses on having cybersecurity insurance as their only safety net:
- Cyber insurance does not reduce the risk of getting impacted by a cyberattack. Instead, it transfers some of the financial risk to an insurance company.
- A policy does not prevent incidents from happening in the first place, nor does it lower the probability of incidents occurring. It is a clear example of risk transfer as opposed to risk reduction
- The cost premium is directly proportional to the control environment. Fewer controls = higher premium
- Cyber insurance policies do not cover all incident-related costs.
- Just like health insurance doesn’t cover every healthcare cost, cyber insurance does not cover every single cost if your clients experience a breach.
- The scope of the coverage may or may not include some very specific items if either:
- The risk was deemed too high by the insurance company due to lack of controls
- The item was omitted to reduce the premium cost
- Security investments can impact cybersecurity insurance costs
- In many cases, implementing strong security controls can reduce cyber insurance premiums. These controls may include multi-factor authentication (MFA), Endpoint Detection & Response (MDR), and secure backups.
- Some insurance companies require certain security controls to be in place before they issue a policy. They may not issue the policy if those specific controls are not met.
- In addition, some businesses implement cyber clauses requiring their vendor partners to maintain specific levels of cybersecurity protection and even carry a certain level of cyber insurance. If your client’s business doesn’t comply, they may lose business or even be held liable for a breach if it originated within their systems.
Example: Business Email Compromise Incident
Your client is a smaller organization with a single accounts payable person.
One day, an email arrives from a known vendor stating that there’s a change to their ACH information for payment remittance.
The request seems legitimate, it’s from the correct point of contact, the change is made, and like usual that vendor’s invoices get paid.
Except they don’t.
The “trusted contact” at the known vendor experienced a Business Email Compromise (BEC) and the attacker was the one talking to AP about changing the payment destination.
All of that money is now gone and in the mysterious third party’s bank account.
If this is not discovered right away, it may be too late to stop the payment.
But this organization has a cybersecurity insurance policy—they should be protected, right?
Unfortunately, if “Funds Transfer Fraud” was not explicitly selected as part of the insurance, the event will not be covered.
While this may have been a cost-saving move for the company or the result of inadequate validation controls, this organization is now left still owing a vendor and losing the money paid to the attacker.
The Takeaways:
- Lesson #1: Not all controls have a cost to implement. Validation that requires accounting staff to call the contact via the phone to verify the update could have potentially stopped the fraudulent change.
- Lesson #2: Encourage your clients to know what their cybersecurity insurance scope is before an incident requires them to call on coverage that they may not have. For fractional CFOs like you, understanding cybersecurity insurance can prove to be a major benefit as you work with clients.
Proactive Cybersecurity Investments
If the pendulum swings too far in the other direction and your clients focus solely on proactive cybersecurity investments, it may lead to similar situations where they don’t have the right level of protection or support that they need.
In most cases, security controls are the counterbalance to user conveniences.
The path of least resistance is often the one chosen, as enforcing too many controls on a user base can have the opposite effect to what was intended.
In an effort to gain back some of that convenience, users may find ingenious ways to work around the control, thereby invalidating the strength it added to the overall security posture.
Example: MFA Exceptions
A medium-sized business has just shifted from on-premises infrastructure to being 100% cloud-based using Software as a Service (SaaS) solutions for file storage, collaboration, accounting, ERP, etc.
The organization implements Conditional Access policies within their collaboration platform to enforce MFA for all accounts. This setup provides a strong unified control environment to protect against opportunistic attackers.
Shortly after deployment, however, it is determined that there is a critical business process that relies on a shared account. The implementation of these controls has made process execution challenging.
To the end users, the security controls make their jobs more difficult to accomplish. They lobby to have an exception for the MFA control, ultimately winning the battle.
Unfortunately, now a single account represents the break in the armor: a shared generic account used for a mission-critical business function that also needs a password that can be easily remembered by all relevant teams.
The result? The account’s password is “sprayed” successfully by an attacker and taken over due to the lack of MFA.
The Takeaways:
- Lesson #3: Decisions about security cannot be made in a silo without an understanding of how the business still needs to function. Your clients can implement controls to simply control themselves out of business.
- Lesson #4: Your security posture is only as good as its weakest component. Conditional Access-enforced MFA is great in concept until there’s an exception to the policy.
Finding Balance
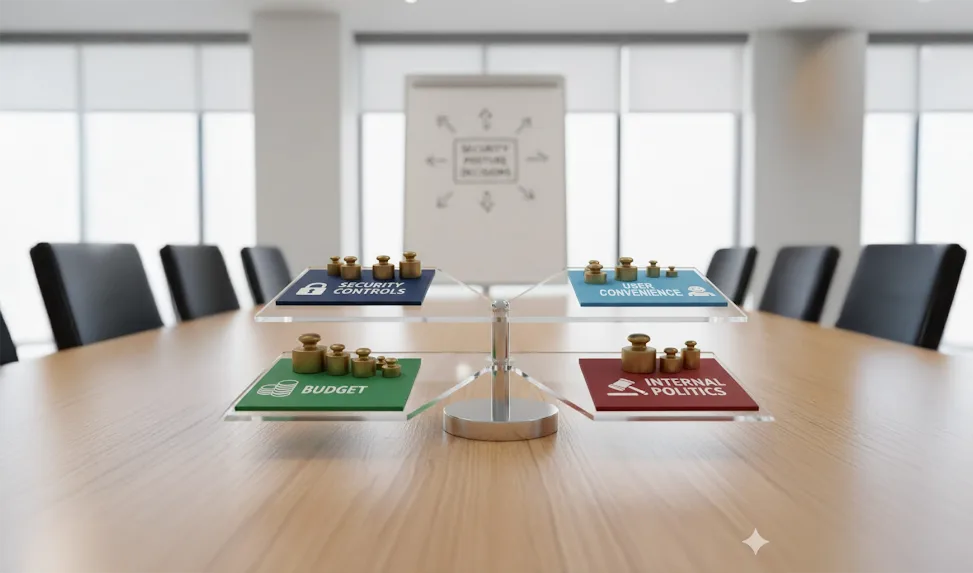
Ultimately, your clients’ security posture decisions need to keep the organization balanced.
Too much in any one direction can offset that balance and lead to financial impact, productivity impact, reputational impact, or, in a worst-case scenario, lead to a business closure.
The question is not “proactive or reactive”— it’s a balance of the two, considering the implications that each has on the organization’s ability to function. Achieving this goal is the core of effective cyber risk management.
Examples of Proactive Controls
Before selecting proactive controls, your clients must understand the actual threats to their organization.
This knowledge is often formed by engaging in a risk assessment and establishing a risk register so that a very clear and objective method identifies the threats, underscores the existing controls, and weighs that threat’s ability to impact the organization.
Only then can practical controls be considered, as the organization can more clearly see where its defenses are weak and where threats are originating from.
| Control | What it does | Why you need it |
|---|---|---|
| Automated Inventory / Remote Monitoring and Management (RMM) Platform | This platform is often used first to create an inventory and subsequently used for the management of organization endpoints. | If an organization does not know what kind of technology assets are present, it cannot adequately know that those assets have been protected properly. |
| Endpoint Protection / Endpoint Detection & Response platform | This platform replaces the more traditionally referenced “antivirus” software and shifts the paradigm to “malicious action” or “anomaly detection.” | Threats have evolved beyond very static descriptions and definitions of what is considered “bad.” Legitimate tools being used in illegitimate ways is as dangerous as the viruses that used to be newsworthy in the early 2000’s. |
| Account Management / Protection – Unique User Accounts – Multi Factor Authentication – Conditional Access – Principle of Least Privilege | This ensures that the users, the largest component of attack surface at any organization, have controls to protect their organization’s digital identities. | Opportunistic attackers spray password lists against anything with an authentication interface every day. While it is not the first line of defense, good account hygiene can often be the last line of defense. |
| Policy Driven Patch Management—Endpoint Operating Systems, Firewall Operating Systems, and Third-Party Applications | This process ensures that patching operating systems or other applications is not done haphazardly, but consistently. Using a policy-driven methodology allows an organization to have confidence that the systems are being patched. | Vendors develop patches often as mitigation for a vulnerability that has been recently identified and can be exploited in their code. Keeping systems up to date ensures that they are as protected as they can be. |
| Vulnerability Scanning Tools and/or services | These processes help balance and confirm that the endpoints are being patched. The patch should remove the indication of the vulnerability or present configuration that could be exploited by an attacker or an insider threat. | Keeping ahead of threats is a challenge; automated tooling can help identify potential targets so that they can be mitigated or find the endpoint that the patch management system has failed on before the attackers do. Many times, this is a function outsourced to a trusted third-party provider. |
| Security Information Event Monitoring tools (SIEM) | The concept is simple—a single location where an organization’s system logs can be exported so they can be analyzed for anomalous behavior or indications of compromise. | This provides both a reactive audit trail and a proactive audit trail since it can be used to match patterns, statistics, behaviors, etc. Many times, this is a function outsourced to a trusted third-party provider. |
| Incident Response Planning | When an incident occurs, it is important to begin addressing it as quickly as possible to minimize the potential impact to the organization. | Following a defined course of action ensures that time is not lost and that the actions support the appropriate response effort due to on-the-spot decision making. |
| Established System Lifecycle – Removal or Retirement of End of Life (EOL) / End of Support Equipment (EOS) | When a system reaches its EOL or EOS status, the vendor typically stops producing patches for identified security vulnerabilities. | This system becomes the break in the armor since there are components that have now become vulnerable and cannot be fixed. |
Each of the above elements carries with it a cost component. As such, that has to be weighed out to make sure that the continuum of security posture is balanced.
Just as each control has a cost component to implement, lack of these controls has a cost component as well whether in terms of the reactive control (cyber insurance, IR Firm, MSSP) or direct cost due to a compromise.
Every Business Thinks They Are The Exception
“This organization doesn’t have anything that someone else should want. We don’t deal with financial services, health information, or government secrets.”
This phrase is often said by an organization to convince themselves NOT to invest in proactive controls.
The reality is that if an organization has money, makes money, or deals with monetary transactions from its customers, it can be and often IS a target.
Financial motive is timeless whether technology was involved or not. However, technology often makes the task easier.
Example: Weak Passwords/MFA
An SMB has team members who do not have MFA enforced for their email.
An account manager with a weak/sprayable password has their account compromised; an unauthorized person now has direct access to this person’s entire mailbox and any other services tied to that collaboration platform.
The attacker sets up some mailbox rules to conceal their actions and may set up forwarding to an external account so that they can keep tabs without having to keep checking that person’s email.
After monitoring the mailbox, the attacker selects a recipient who receives mail often enough to suggest a “good relationship,” yet rarely enough that a slight change in tone wouldn’t be noticed.
The attacker emails that AP person at the other organization with updated instructions on how to remit payment due to a change in the bank account.
The changes are made, the money is sent, and the attacker walks away with a payday, leaving quite a wake in the process with both entities.
The Takeaway:
- Lesson #5: You may not always be the target. It may be that you are the weapon used against your clients or vendors.
Examples of Reactive Controls
In keeping with the theme of balance, reactive and response controls are as necessary as proactive controls in maintaining a strong security posture.
A risk assessment should help to identify areas in which the controls are deficient. This evaluation includes not only preventative controls designed to reduce the likelihood of an incident, but also the response actions necessary to manage one.
| Control | What it does | Why you need it |
|---|---|---|
| Cybersecurity Insurance | When there is a security incident that is covered by the policy, it provides both avenues for financial reimbursement as well as support in the response actions. | Most, if not all, cybersecurity insurance carriers maintain relationships with MSSPs or IR firms as well as legal counsel to ensure that the response actions follow a legally protected course of action. |
| Managed Security Services Providers | An MSSP is to the security posture as a Managed IT Services Provider is to traditional break/fix helpdesk support. | The MSSP’s primary role is specific to security posture. Often, an MSSP’s services include providing some of the proactive services such as Vulnerability Scanning or SIEM in addition to having a response team or Security Operations Center (SOC) available to triage an incident. |
| Incident Response Firm – On Retainer | An IR firm, unlike an MSSP, may only focus on the response actions. Insurance carriers often will bring in an IR firm, but organizations can establish their own relationships as well. | The IR firm can often make up the gap in response action where the organization is lacking. Unlike an MSSP, it may not have as high a recurring cost since it is more about being “at the ready” versus an active role. |
Similarly to proactive controls, the reactive ones have their own cost as well. This is also often a case of “you get what you pay for,” though the most expensive may not always be the best.
The Decision: In-House Staff vs. MSSP
An organization has just experienced a security incident.
A compromised VPN account allowed an attacker to traverse the network laterally and identify high-value targets, which are then targeted with a ransomware attack.
In the wake of the incident, the organization needs to evaluate where the controls had shortcomings.
The incident made the organization aware that their lack of any/enough security-knowledgeable employees may have been a contributing factor.
How does an organization decide on the course of action to take?
Hiring or training staff to become security experts is neither cheap nor easy, and often leaves organizations with “all their eggs in a single basket” when one person has that job role.
Consider this: Arctic Wolf found that the cost of building a fully staffed, 24/7 Security Operations Center (SOC) could average more than $1 million annually.
Alternatively, an MSSP or an IR firm may present a more cost-attractive solution for what can be provided.
When factoring in the costs associated with in-house staff members, after salary, benefits, and intangible costs are included, an MSSP is usually a more appropriate direction to take—especially for SMBs.
MSSPs will have teams of staff members with built-in redundancies so that there are multiple eyes on the control environment and/or multiple responders to an incident.
The organization must weigh the lower cost of an employee with the benefit of having an entity to turn to with the expertise at their fingertips and the capability to respond quickly when an incident occurs.
The Takeaway:
- Lesson #6: Cost will always be a factor. Don’t overlook a small cost differential for a large skill differential.
Next Steps
Now, your clients have an important decision to make: what do they invest in for the best cybersecurity ROI?
This is not a dissimilar question even outside of the context of security. This is also not a decision that should be made purely by dollars and cents, but instead with proper consultation.
Work with a Trusted Insurance Company
A trusted insurance agent can help to steer your clients in the right direction as far as coverage is concerned for cybersecurity insurance. As a fractional CFO, understanding this direction can help you build a clearer picture of overall risk.
Don’t guess, ask the expert. See if they can cut through the lingo and go straight to some examples of “when a situation like this occurs, what coverage is provided?”
Work with a Trusted Expert
A trusted subject matter expert or cybersecurity company can provide guidance on specific technologies or technological controls.
You are going to an SME because you aren’t one, so don’t hold back a question because you believe you should already know. A good SME will take the time to explain.
While discussing, don’t hesitate to bring up scenarios so that you can better see and understand how the control defends the organization from the threat.
Oftentimes, you can leverage a trusted SME to aid in the risk assessment process and help identify the threats that need defense based on the organization’s controls.
Take a Thorough Approach
Avoid buzzwords—there are many of them. There are often claims of “conceptual controls” that have no actual bearing on the reality of the security posture. They can present a checkbox or a false sense of good posture.
Always examine all of the options, because there are no one-size-fits-all security solutions or controls. What works for a large enterprise may fail miserably in a small-to-medium sized business.
You can implement enough controls to control an organization out of business, or to trigger a mutiny from the staff.
Your clients should choose the appropriate proactive and reactive controls to create a reasonable cyber resilience strategy that shields them from attacks while providing meaningful coverage in the event of an incident.
Choosing only proactive controls or only reactive controls could open them up to a host of risks.
Remember: security posture is all about balance.
Next steps, in summary:
- Work with a trusted insurance company and rely on their focused expertise
- Select a reputable cybersecurity company to help you assess risk and implement controls
- Take an in-depth approach, avoiding jargon that can present a false sense of good posture
- Examine all of the options available to you instead of relying on a one-size-fits-all solution
- Ensure the continuum of security posture is balanced by combining proactive and reactive controls